How links work (and why netplex injects no traffic)
A link in netplex. is not a drawing - it is a real Linux data path. When you connect two nodes, netplex. builds a small two-port virtual bridge for that link and adds one veth (a virtual cable end) to each node. That is the whole wire: the two devices, and nothing else.
This matters because of a promise netplex. makes: it injects no traffic of its own. Capture on any link and you see only your nodes' own frames - never a netplex-generated packet. This page explains the model and why that guarantee holds.
Draw a link between two nodes and that is a real wire. Nodes start with only loopback - a Docker node boots network_mode=none - and get exactly the interfaces you draw. There is no hidden management network and no auto-assigned IPs; the topology on screen is the whole network.
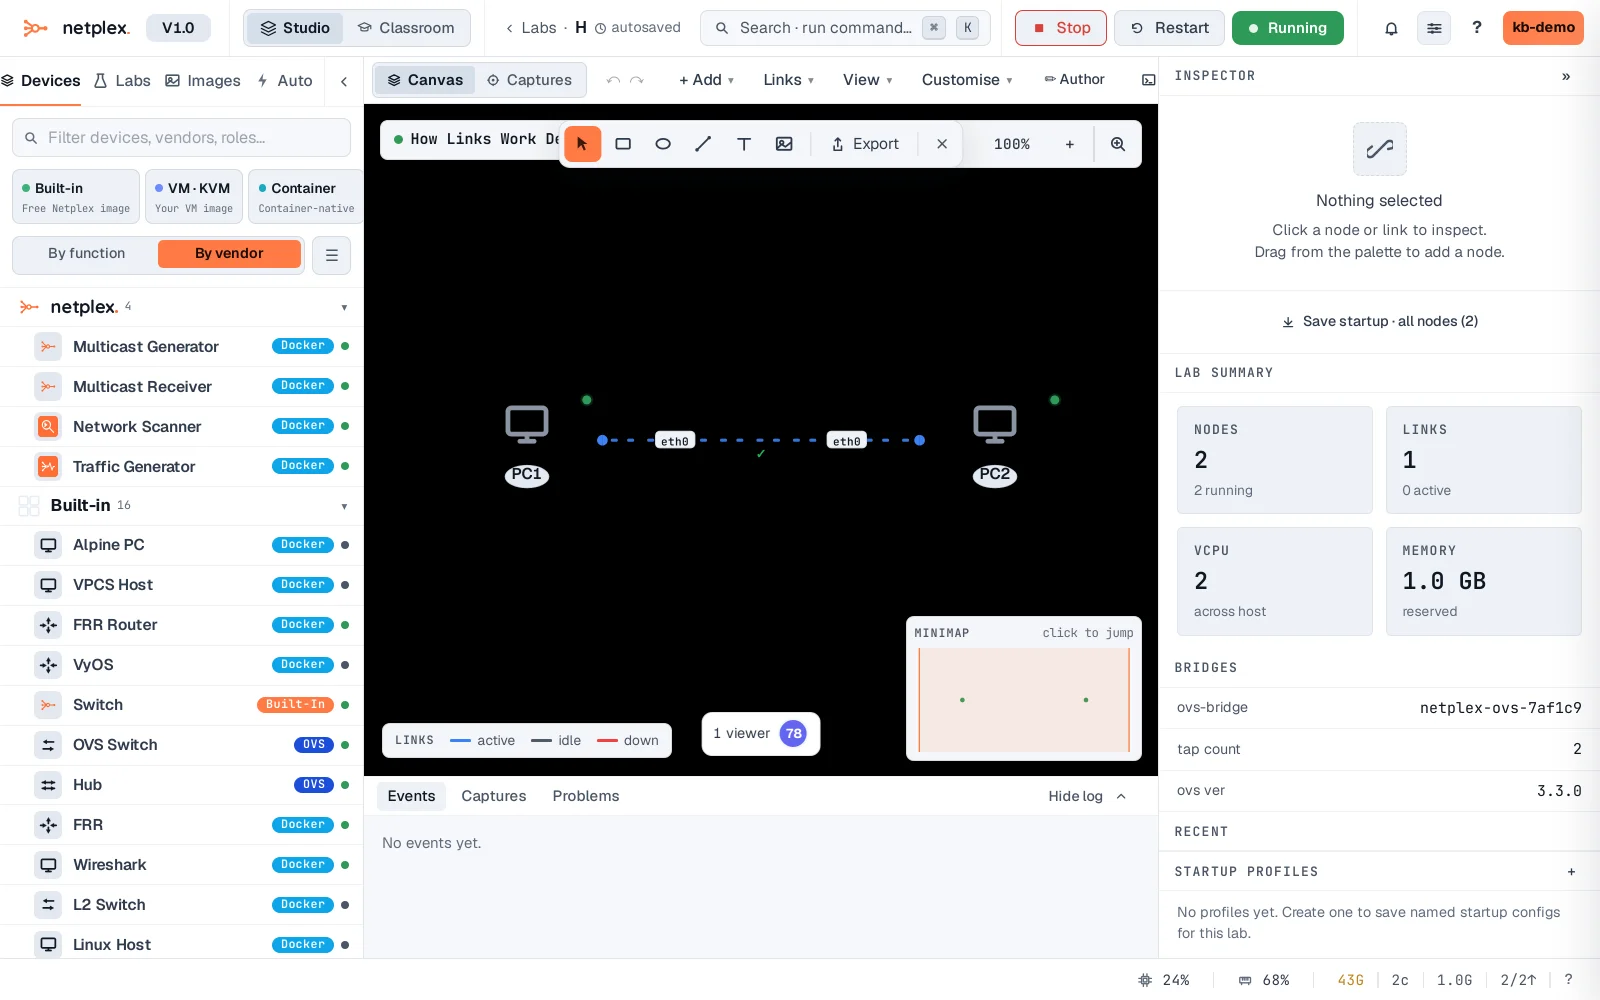
Click the link to inspect it. Each link is independently managed: its two endpoints, a Data plane, an admin state you can suspend without deleting, and directional QoS (shape A→B differently from B→A). Behind it sits a dedicated two-port bridge - one bridge per link, so links never leak into each other.
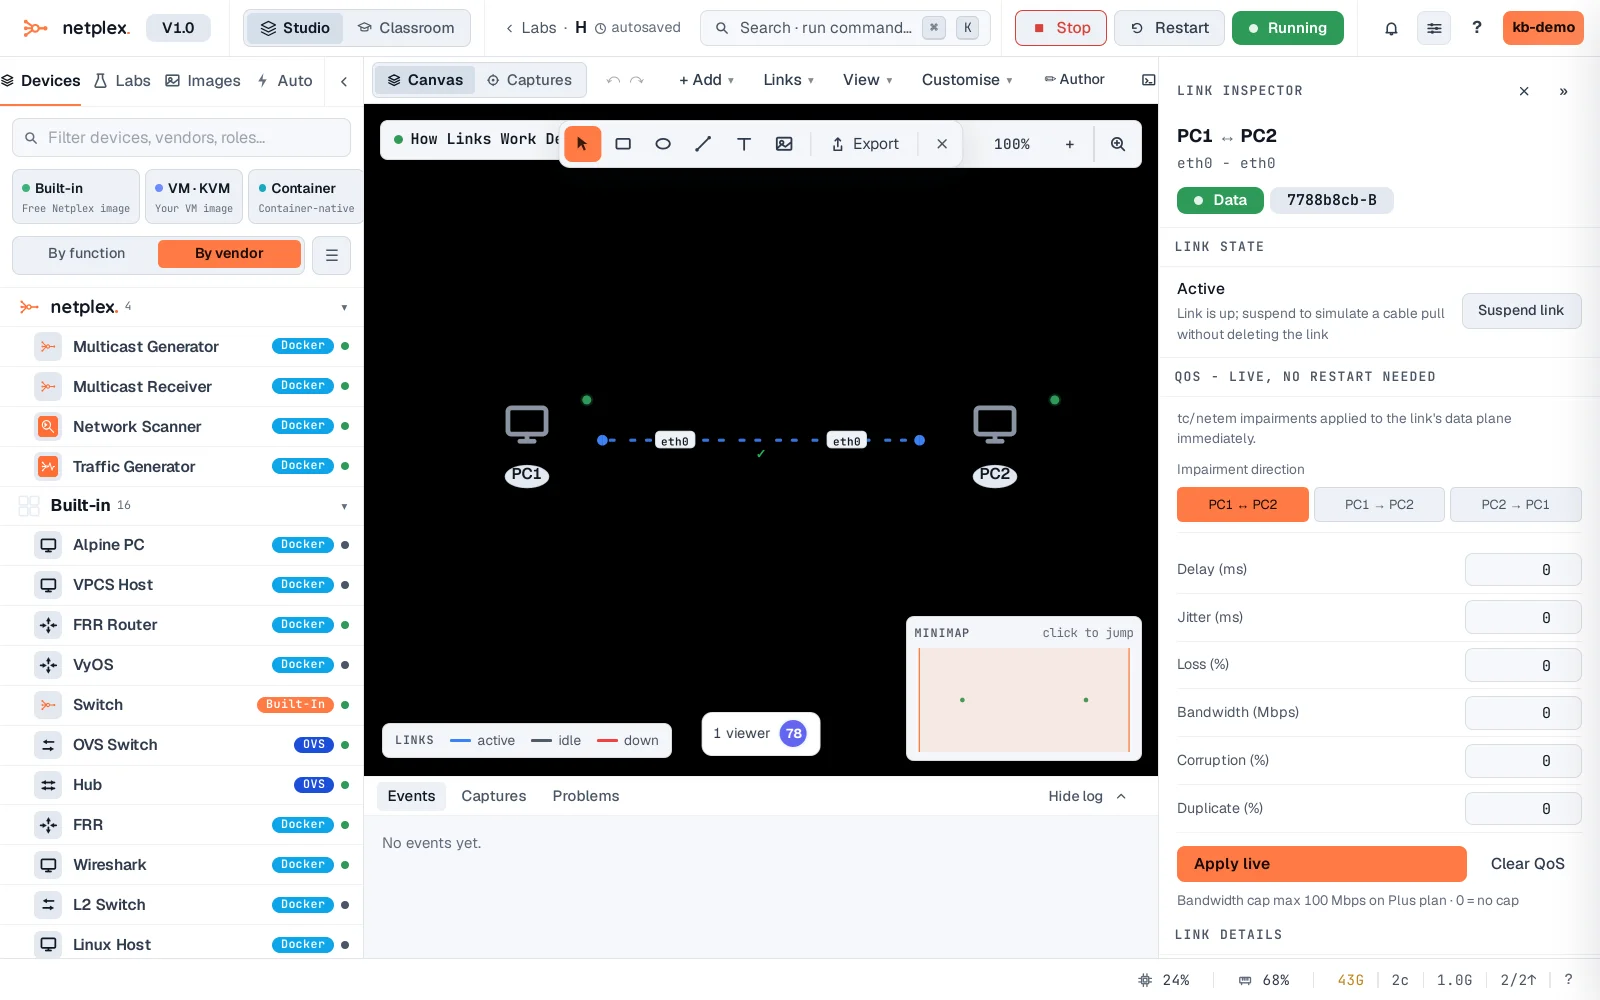
The zero-injection guarantee: that per-link bridge and the unmanaged switch add nothing to the wire. The bridge turns IPv6 off before it comes up (so it sends no IPv6 chatter), runs no spanning-tree, and sends no IGMP/MLD queries (multicast group questions). So a packet capture on this link shows only what PC1 and PC2 send - your traffic, nothing synthetic. (A node's own OS traffic, like its DHCP or IPv6, is the node's - that is allowed; it is netplex. that stays silent.)
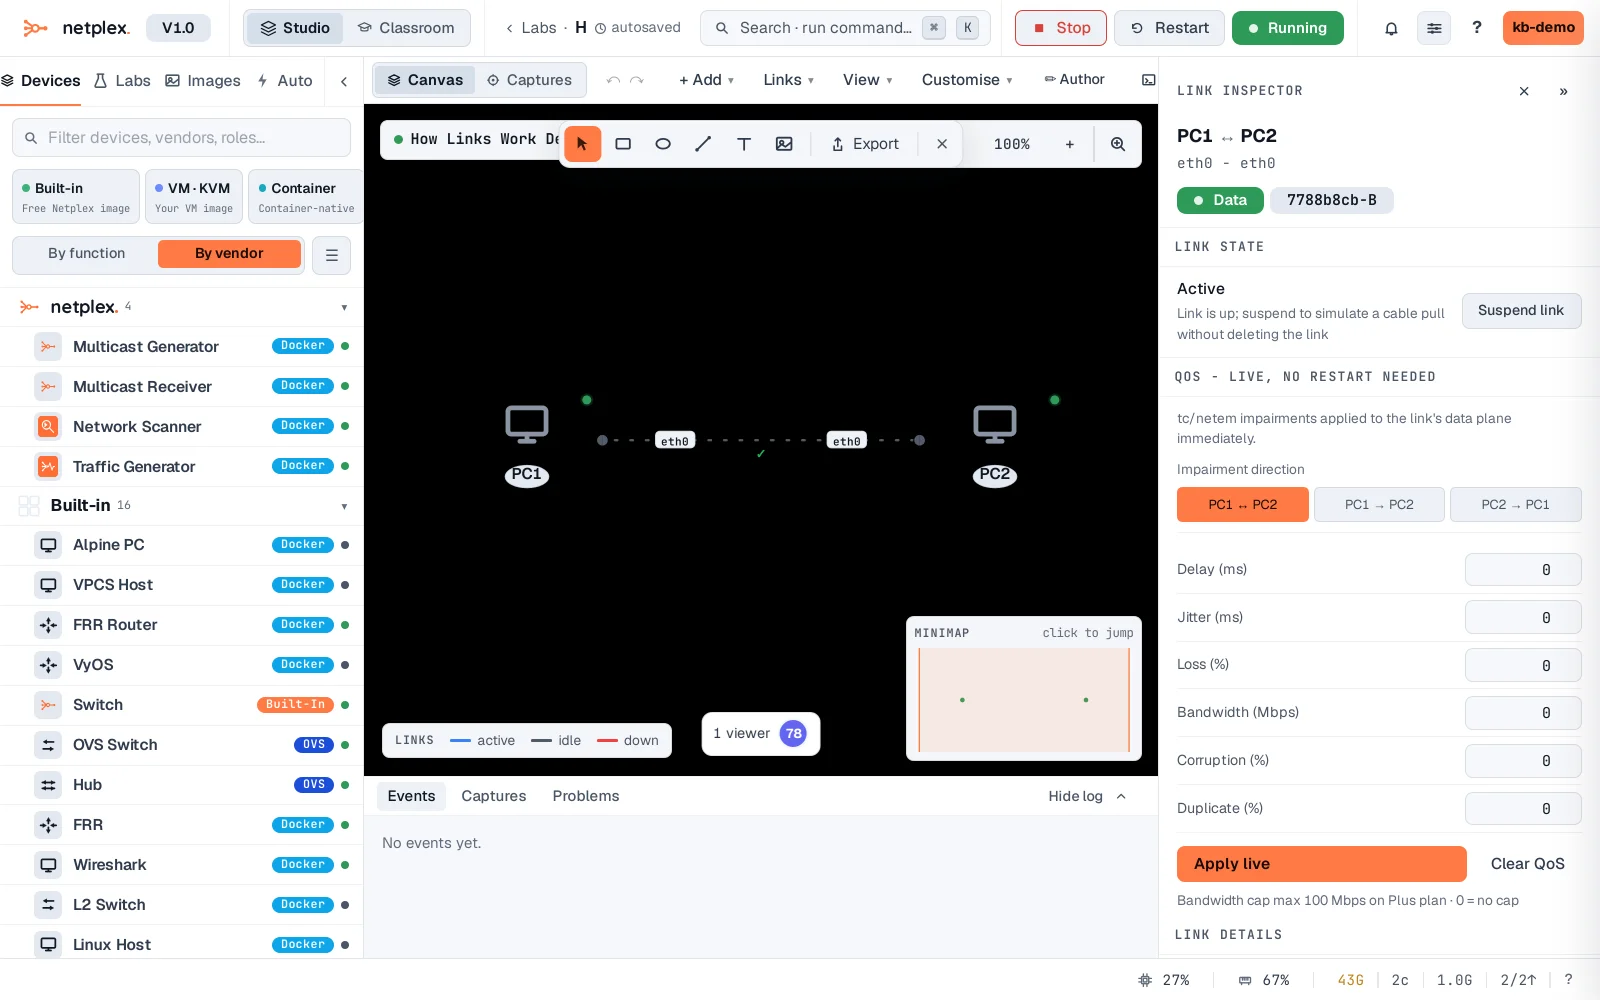
Because links are real data paths, everything downstream is real too: QoS is Linux tc/netem on the wire, link stats are counted off the bridge, and a capture is a genuine tcpdump. netplex. also refuses loops between switches (L2 loops) when you draw them, instead of hiding them with spanning-tree (a protocol that blocks loops). To see the zero-injection guarantee for yourself, attach a packet capture to a link and read the frames - see the packet-capture guide.